Industries · Healthcare
One unverified clinical claim can cost you the bid.
Health system RFPs, HIPAA security questionnaires and vendor risk assessments all ask for the same evidence. Tribble answers them from what your clinical, security and legal owners already approved, and sends only the new questions back to them.
- 3.1Will you sign a Business Associate Agreement? LegalApproved answer, reused
- 3.4Describe how PHI is encrypted at rest and in transit. SecurityApproved answer, reused
- 3.9Provide your latest SOC 2 Type II report or HITRUST certification. SecurityApproved answer, reused
- 5.2Which EHRs do you integrate with, and over which standards? ProductApproved answer, reused
- 7.1Summarize published clinical outcomes for this product. ClinicalNew, sent to its owner
The documents health system buyers send.
Grouped by who owns the answer. Every one draws on the same approved material.
| Document | What it asks for | Answer it with |
|---|---|---|
| Security and privacy | ||
| HIPAA security questionnaires | PHI handling, encryption, access control and breach notification | Security questionnaires → |
| Vendor risk assessments | Health system third-party risk reviews, often run through platforms such as Censinet or CORL | Security questionnaires → |
| HECVAT | The standard assessment academic medical centers send | Security questionnaires → |
| Legal | ||
| Business Associate Agreement terms | Subcontractors, breach timelines, data return and destruction | RFP automation → |
| Clinical and product | ||
| Health system RFPs and RFIs | Clinical value, EHR integration, implementation and pricing | RFP automation → |
| Value analysis requests | Outcomes, peer-reviewed evidence and questions from the value analysis committee | Proposal automation → |
| Commercial | ||
| GPO and IDN vendor onboarding | Contracting, pricing tiers, insurance certificates and supplier forms | RFP automation → |
Three buyers, three different reviews.
Health systems and IDNs
Supply chain runs the RFP. IT security and the value analysis committee each review their own sections, on their own timelines.
- They send
- RFPs, HIPAA questionnaires, vendor risk assessments
- They check first
- EHR integration, security posture, clinical evidence
Payers and health plans
Plans and benefits buyers score vendors on member outcomes, data handling and reporting, often through a consultant.
- They send
- RFPs from plan sponsors and consultants, privacy and security reviews
- They check first
- Member data handling, reporting, service levels
Academic medical centers
Procurement follows university rules, so the security review usually arrives as a HECVAT.
- They send
- HECVAT, research data questions, RFPs
- They check first
- Research data controls, accessibility, security documentation
One question, start to finish.
What happens to a single question when a HIPAA security questionnaire lands.
The question
Describe how you encrypt PHI at rest and in transit, and how encryption keys are managed.
Example: HIPAA security questionnaire, owned by your security lead
- 01
It comes in
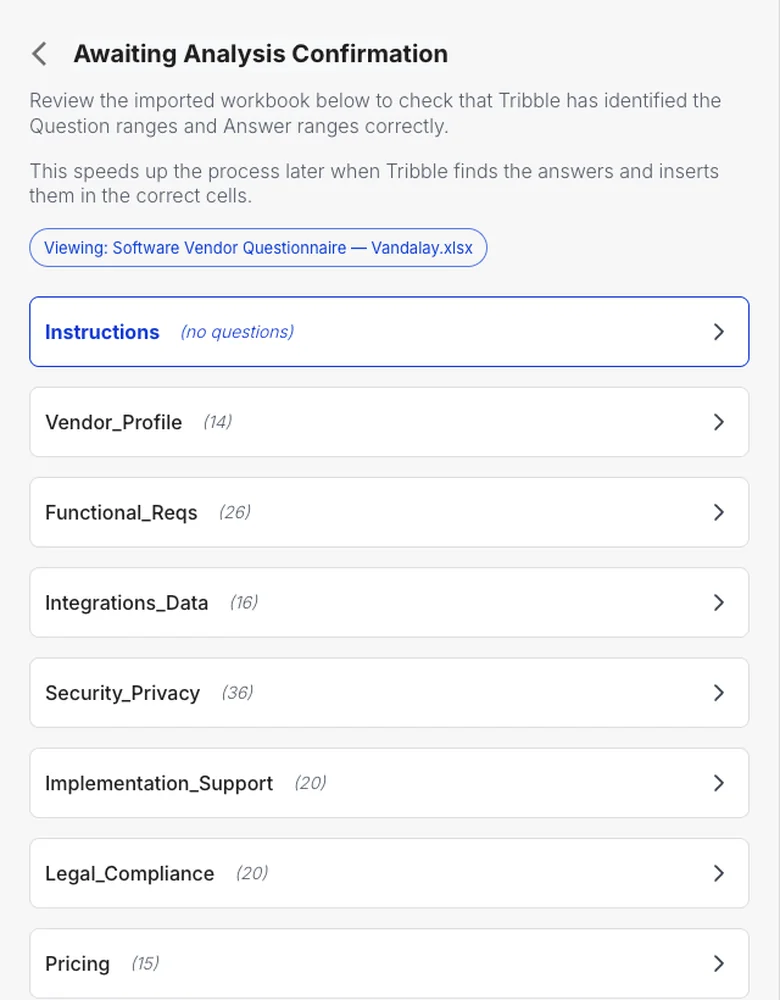
The questionnaire arrives as the buyer’s spreadsheet or through their portal. Tribble reads every row, including the ones hidden in merged cells.
- 02
Tribble drafts it
It matches the question to your approved encryption answer and drafts a reply in the buyer’s wording.
Sourcesecurity policy, section 4. Owner: your security lead. - 03
Only what’s new gets reviewed
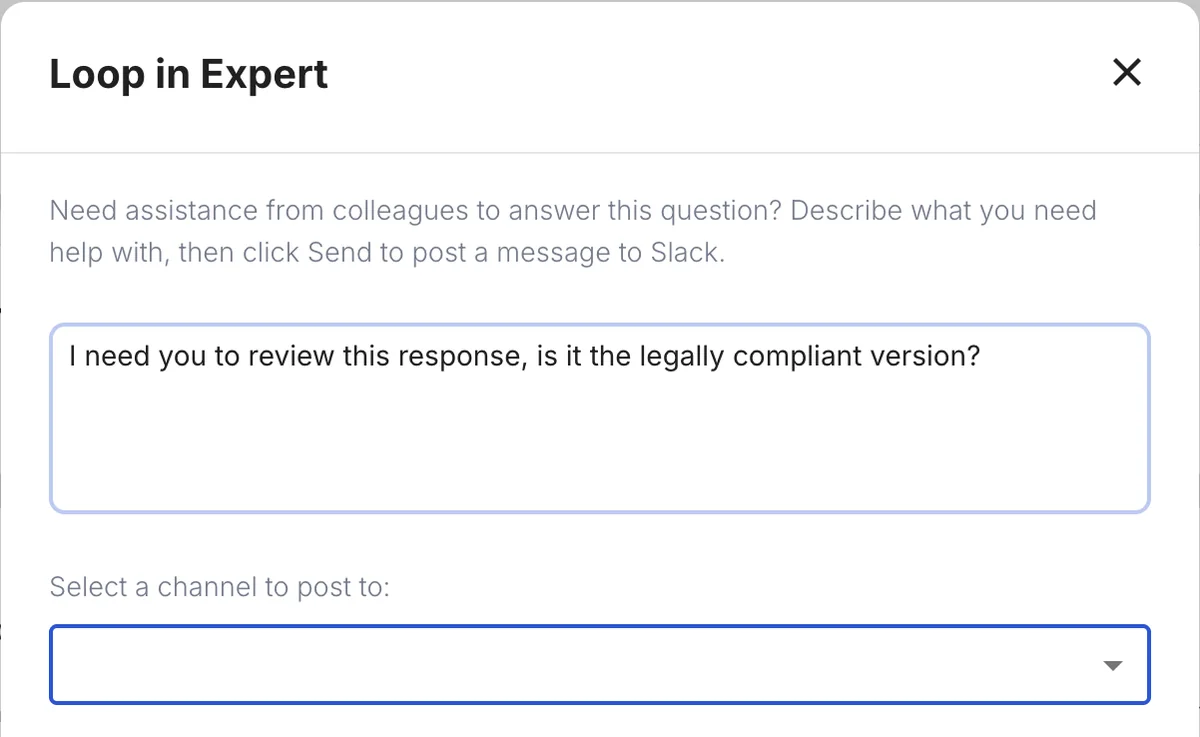
Your key management process changed last quarter, so this answer goes to your security lead with the change marked. Answers that matched go straight through.
- 04
It goes back in their format
The finished answers go back into the buyer’s own file, ready to submit.
What it looks like in Tribble Respond.
The same answers, in the rep’s hands before the call.
Tribble Engage puts your approved answers where sellers already work, in Slack and Teams. A rep asks in plain English and gets the approved answer with its source, so nobody guesses about BAA terms on a call with a CISO.
Tribble Scribe records the call, drafts the follow-up and updates the CRM.
Example · Slack
@Tribble does our BAA let us use subcontractors for hosting?
Yes. Your standard BAA allows subcontractors who sign equivalent terms, and your hosting provider is listed in its appendix.
Sourcestandard BAA, approved by LegalMapped to the frameworks health system reviewers use.
- HIPAA Security RuleAdministrative, physical and technical safeguards
- HITRUST CSFCertified controls, and which ones you inherit
- SOC 2 Type IITrust services criteria and the report itself
- HECVATAssessments from academic medical centers
- HL7 v2 and FHIRIntegration and interoperability questions
- NIST CSFSecurity program questions
Tribble answers from your own evidence for each framework. Tribble itself is SOC 2 Type II compliant.
It learns from the tools your team already uses.
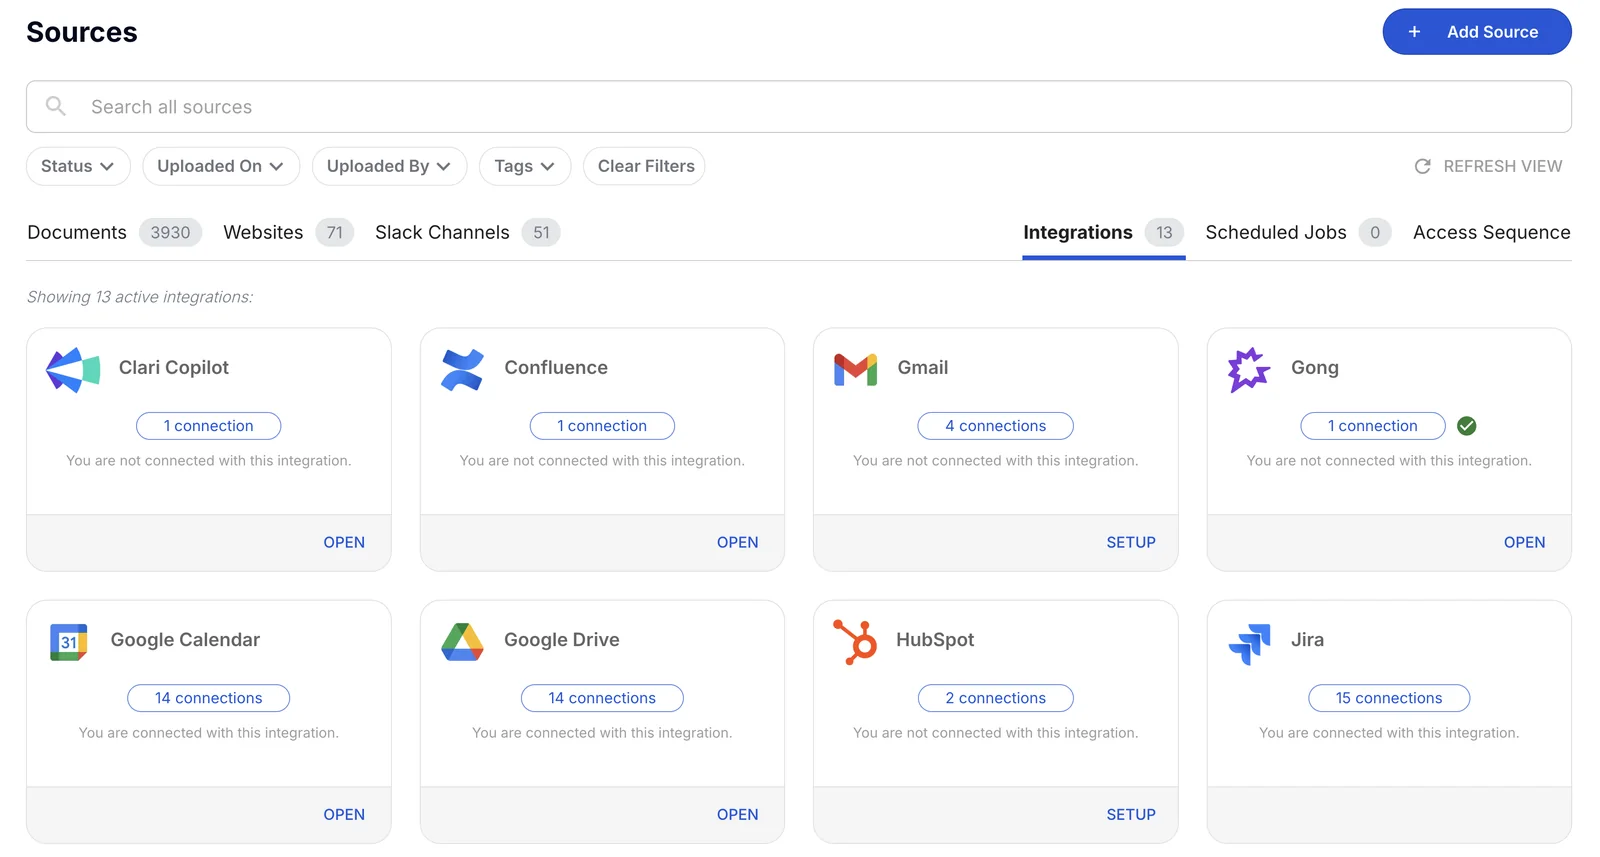
Security policies in SharePoint, past RFPs in Google Drive, clinical evidence in Confluence, deal notes in Salesforce. Tribble connects to them and keeps each one’s permissions.
Why general-purpose AI isn’t enough for health system RFPs.
| Compare | Generic AI | Tribble |
|---|---|---|
| Answers from | Public training data | Your approved answers and current controls |
| Clinical claims | No link to what was approved | Tied to the approved claim and its owner |
| Security evidence | Paraphrased from memory | Linked to your current SOC 2 or HITRUST documents |
| When a control changes | Nothing updates | Update it once and the next response uses it |
| Review | Check everything, or nothing | Only new or changed answers go to their owner |
| Audit trail | None | Who approved each answer, and when |
From a healthcare team on Tribble.
Customer story · Healthcare benefits
How Rightway put expert hours back into member care
“I put this in Tribble, and within like five minutes, I had a beautiful response.”Sales manager, Rightway, as relayed by Gabrielle Rahn Read the Rightway story →
Rated by the teams that use it.
Fall 2026, across RFP, AI Sales Assistant, AI Meeting Assistants, AI Proposal Generator Tools and Sales Analytics. Read the reviews on G2 →
FAQ
Common questions.
Does Tribble touch PHI?
It doesn’t need to. Tribble works from your proposal content, security documentation, approved claims and past responses. Each source keeps the permissions it already had, so people only see what they’re allowed to see.
Is Tribble HIPAA certified?
There’s no official HIPAA certification for any vendor. Tribble is SOC 2 Type II compliant, and it answers HIPAA questions from your own security documentation, with the source attached.
How do we stop a clinical claim drifting from what was approved?
Every answer comes from an approved source and shows where it came from, who owns it and when it was last approved. When your clinical or regulatory team changes what can be said, you update it once and the next response uses the new version.
Security questionnaires arrive late and hold up the deal. Does this help?
That’s where most teams start. Answers that match your approved controls come back with their source, and your security lead only reviews what’s new or changed.
How is this different from the response library we already have?
A library stores answers. It can’t tell which ones are out of date, or which contradict a control that changed. Tribble tracks the source, owner and version of every answer, and sends anything it isn’t sure of to the right person.
Bring a real HIPAA questionnaire.
Send a redacted one, or a recent health system RFP. We’ll answer it from your own material on the call, and show you which questions would go to your security and clinical owners.
Book a working session